Google previews MPC crypto custody service for banks
Google Multi-Party Compute splits private keys across separate systems and checks policy before signing. It is in private preview, with launch set for early 2027.
CryptoGroup Newsroom · · 2 min read
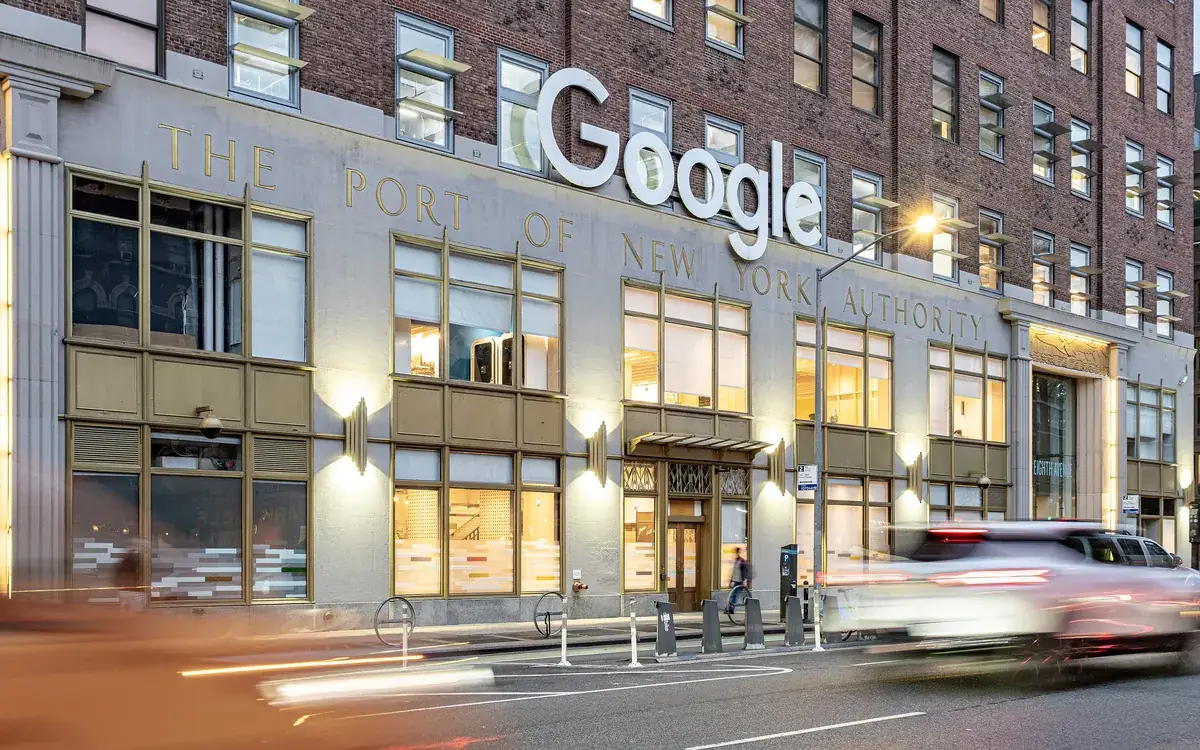
Google is showing financial institutions a custody system for crypto that never puts a whole private key in one place. The product, Google Multi-Party Compute (MPC), was due to be presented on Wednesday at Google's first digital assets symposium in New York, CoinDesk reported. It is in private preview, being tested by several unnamed design partners and large financial institutions, and Alphabet already uses it to protect its own assets on Ethereum and Solana.
How it works
Whoever holds a wallet's private key can move the funds, and blockchain transfers usually can't be reversed. Our guide to what a private key is explains why. MPC tackles that single point of failure:
- Split key. The key exists only as fragments spread across separate systems; several of them must cooperate to sign a transaction.
- Rules before signing. Each transaction is checked against the institution's policies, such as limits or required approvals, before it is signed.
- Customer control. Google says clients keep control of their key material, and it cannot see the shares unencrypted even when they sit on Google infrastructure.
- Recovery. Signing, policies and key recovery come as one service instead of parts that clients wire together themselves.
Google already offers Cloud KMS and Cloud HSM for key management and published MPC design guidance in 2023, but says this is its first dedicated MPC custody product. It plans commercial availability in early 2027 and has not disclosed pricing. For how banks and exchanges hold coins for clients, see what is crypto custody.
Why now
Key theft is the industry's costliest weakness. Chainalysis found that compromised private keys accounted for 43.8% of crypto stolen in 2024, and DeFiLlama data shows about 40% of the $16.69 billion lost to hacks and exploits through June came from key compromises. "Digital asset adoption and tokenization are at an inflection point," said Rich Widmann, director of digital assets strategy at Google Cloud.
Google also pitches the service against AI-assisted attacks and, later, quantum computers, saying it can eventually support post-quantum cryptography. For now its protections target stolen credentials and unauthorised transactions, not a break of the underlying math. Weak keys are a live issue: last week researchers cracked eight weak eMudhra certificate keys. One limit remains: policy checks can't stop an authorised employee who is tricked into approving a malicious transfer.
This article is for information only and is not financial advice. Crypto assets are volatile; do your own research. Read our disclaimer
More from Security
View all →Read next
What is Zcash (ZEC)? How its shielded privacy works
Zcash explained: how shielded and transparent addresses work, zk-SNARKs, the 21M ZEC supply, the 2026 Orchard bug and Ironwood fix, and Zcash vs Monero.
Euronext halts CoinShares Zcash ETP on debut day
Euronext suspended CoinShares' Zcash ETP (ZCSH) in Paris on the day it was due to list, citing settlement support at the central securities depository.
OKXICE objections hit 33: JPMorgan, Coca-Cola, Dell opt out
JPMorgan, Coca-Cola, Dell and four more firms objected to tokenized trading of their shares on OKXICE, lifting the total to 33 and nearly half the first list.